Kafka Security Flaw Could Let Attackers Fake a Login
LinuxSecurity linuxsecurity.com
This is what was read here when it was published. LinuxSecurity Editors no longer carries it in what it publishes now.
Aurekai listening
Listen to this summary
Original instrumental score; voice stays in front.
Ready to listen
This reads the text available on this page using your browser's voice. It is not a publisher-recorded narration; voice processing depends on your browser.Some Apache Kafka servers could accept a made-up identity and give an attacker access as that user.
More ways to use this
Open on another device

Scan to open this page. Your saved notes and account access are not included.
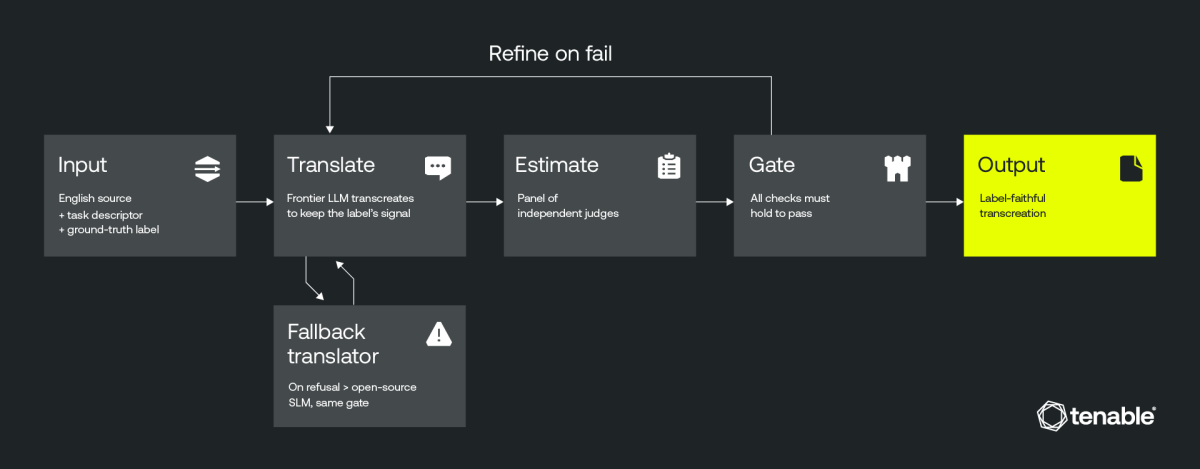 How Tenable brought multi-language support to security detectors with agentic translation