Open Source vs Commercial Email Security: Operational Choices and Risks
LinuxSecurity linuxsecurity.com
Aurekai listening
Listen to this summary
Original instrumental score; voice stays in front.
Ready to listen
This reads the text available on this page using your browser's voice. It is not a publisher-recorded narration; voice processing depends on your browser.Email still looks like plumbing until it becomes the incident timeline, which is why the enterprise email security decision tends to surface only after something slips through and everyone is suddenly counting minutes. By then, the question is no longer about preference or tooling taste; it is about whether the system bends under pressure or holds.
More ways to use this
Open on another device

Scan to open this page. Your saved notes and account access are not included.
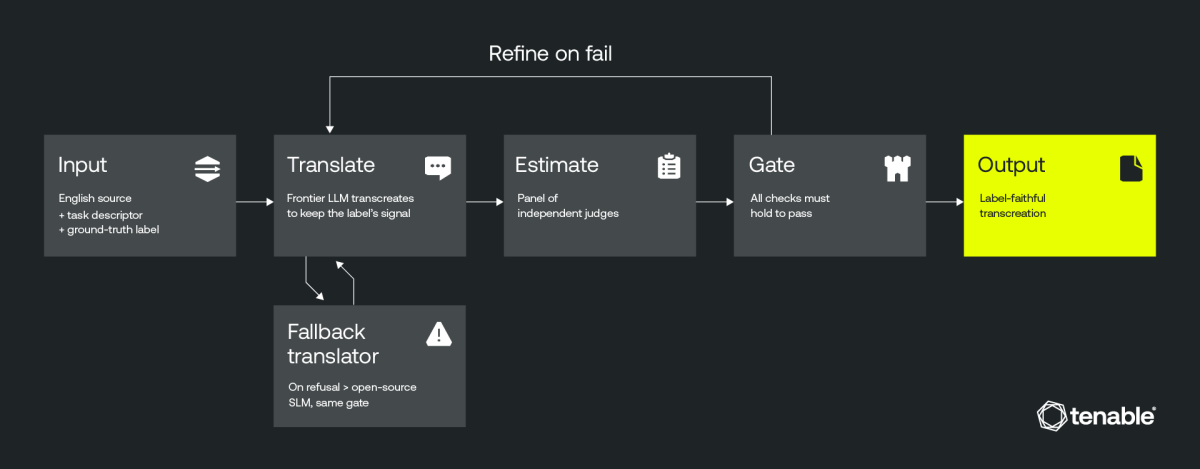 How Tenable brought multi-language support to security detectors with agentic translation