CVE-2026-99318 — In the Linux kernel, the following vulnerability has been resolved: ALSA: bcd2000: Fix use-after-free of MIDI URBs on file close bcd2000_d
ThreatFilter threatfilter.dev
Listen to this summary
(vendor/severity tags below are heuristic) In the Linux kernel, the following vulnerability has been resolved: ALSA: bcd2000: Fix use-after-free of MIDI URBs on file close bcd2000_disconnect() calls snd_card_disconnect(), which only prevents new opens, and then frees the MIDI URBs. A rawmidi file that was already open can still be closed afterwards, and its close callback, bcd2000_midi_output_close(), calls usb_kill_urb() on midi_out_urb. The URB pointers are cleared on disconnect and their accesses are serialized with midi_lock, but bcd2000_midi_output_close() reads midi_out_urb without that lock. The check can therefore pass just bef
More ways to use this
Open on another device

Scan to open this page. Your saved notes and account access are not included.
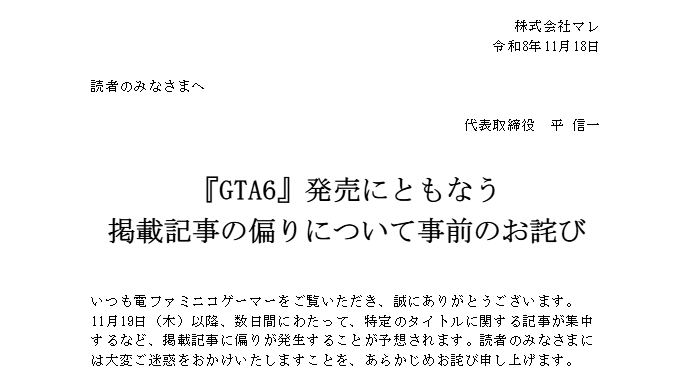 Denfaminicogamer releases an advance apology for the imbalance in article coverage following GTA 6's release
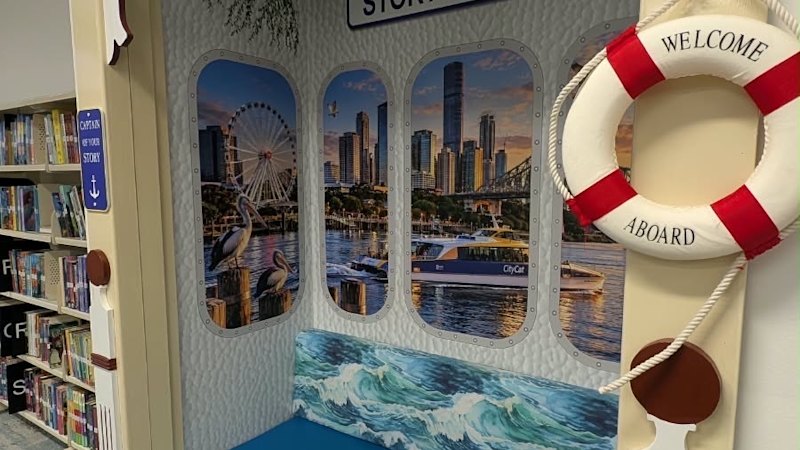 Call to regulate AI use in public art after Brisbane mural backlash
 Police probe after teacher allegedly sold drugs and alcohol to students
 Java4Shell (CVE-2026-114938): Frequently asked questions about OpenJDK remote code execution vulnerability
 U.S. urges critical infrastructure orgs to secure refrigeration systems ASAP after EU supermarket and blood bank attacks